




Updated 12 November 2026 · luckycloud editorial team
The personnel file is stored on a server in Germany. But its sharing link is still in the former project team's group chat. This is how privacy can fail in everyday work even when the storage location is right.
Using a cloud service in compliance with the GDPR takes more than a German server: you need an appropriate agreement, clear safeguards and access permissions that match the way you work. Whether you may process the data remains a separate question. Cloud storage cannot make unlawful processing lawful.
1. The data processing agreement: Who is responsible for what?
If your business determines the purposes and essential means of processing, it is generally the controller for that processing. A cloud provider that processes personal data on your instructions acts as a processor for that work. Article 28 GDPR requires a data processing agreement, or DPA, for this processing.
The agreement should explain which data is processed, which other service providers are involved and how the provider helps you fulfil your data protection obligations. It must also address returning or deleting data when the contract ends and making evidence available for verification.
When choosing a provider: Ask for the DPA before you start. Check that it covers the service you are buying and how you will use it. A signed document does not replace a lawful basis for processing or appropriate settings.
2. Data location: Where does processing actually happen?
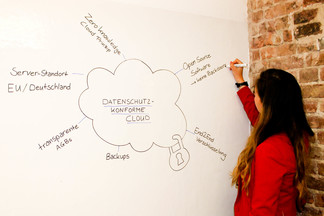
Storage location matters. Also ask about backups, other service providers and possible access from other countries. A location in Germany does not fully answer these questions.
If personal data is transferred to a country outside the European Economic Area, the requirements of Chapter V GDPR must also be assessed. Such transfers are not prohibited across the board. The provider should clearly explain the proposed transfer arrangement and the safeguards it relies on.
A useful question: “Does your location statement also cover backups and the other service providers processing my data?” Keep the answer with your selection records.
3. Technical and organisational measures: What protection fits your data?
Technical and organisational measures, often abbreviated to TOMs, describe the practical protection of processing. Article 32 GDPR requires a level of security appropriate to the risk. Measures can include encryption, access controls, recovery and regular checks of their effectiveness.
A public brochure and personnel records may need different precautions. Ask specific questions: Who may open the files? Who can decrypt them? Which sharing arrangements are intended? What happens if a device is lost or someone leaves the business?
The scope of encryption matters too. Transport encryption protects data in transit. With end-to-end encryption, the endpoint devices and control over the keys are among the critical factors. An already decrypted local copy does not disappear when you later revoke a cloud share.
4. Check cloud access with three test files
Before rolling out the service, create two test files: one for internal collaboration and a second in a separate directory for an external partner. Internally, one person may edit and a second may only read. The third file is created after access has been revoked. Use fictitious data throughout.
- Check permissions. Sign in with each test role. With the read-only account, also try changing a file. Try opening a directory that the role should not be allowed to access. Check the access methods you actually use, such as a browser, sync client or WebDAV.
- End access. Revoke the external directory share or block the test account using your planned procedure. Reopen the old link. Then create the third test file in the previously shared directory from another authorised account. Is it still available through the access you revoked? Assess previously downloaded files separately.
- Recover a file. Change or delete a test file and recover it using the intended procedure. Record who can do this and any limits or retention periods.
Record the result, the responsible person and any unresolved points. This small trial checks your specific workflow. It does not replace a full security assessment, but it shows whether your planned rules work in practice.
5. Do you need a data protection officer?
Under section 38 of Germany's Federal Data Protection Act, non-public bodies in Germany generally have to designate a data protection officer if at least 20 people are constantly engaged in the automated processing of personal data. Other requirements can apply regardless of that number, including under Article 37 GDPR and for certain processing under section 38.
The role may be fulfilled internally or externally under a service contract. Expertise, sufficient resources and avoiding conflicts of interest are essential. A business without a duty to designate a data protection officer must still meet its data protection obligations.
How to assess luckycloud
You can read our current DPA (German PDF) before you start. The associated current technical and organisational measures and subprocessor list are available to download in the customer dashboard. Available features depend on your service and plan.
Our guides to sharing, data recovery and encrypted directories can help with your trial. Choose a workflow that actually occurs in your business. If questions remain, clarify them with us before moving confidential data.
From the archive: Our 2019 GDPR interview
This conversation with Fresh Compliance is a historical contribution marking the first anniversary of the GDPR. Some legal information is outdated: the ten-person threshold for a data protection officer shown in the video no longer applies. Use the updated guide above for the current explanation.
German · 9:06 minutes · Original recording from 2019. The updated guide provides a written explanation of the topics discussed here. A complete subtitle track is not available for the archive recording. Original article: Christina Gluch.